
One senior point of contact
Continuity from first diagnosis to implementation and assurance.
Governancy helps growing and mid-sized organisations translate regulatory and assurance pressure into governance they can actually run, supported by senior continuity and no mandatory tooling.
Complexity often enters through the consultancy model itself: too many workstreams, too many templates and too many people. Governancy is designed to keep the control model clear.
Continuity from first diagnosis to implementation and assurance.
Start with ownership, decisions and operating evidence. Documentation follows the system.
Use enough structure to control material risk without creating a compliance industry.
Use existing systems where they work. Introduce technology only when it solves a real operating problem.
Governancy brings together experience in cybersecurity, executive management, auditing and legal compliance. We consider challenges not only through standards and regulations, but also through management accountability and practical implementation.
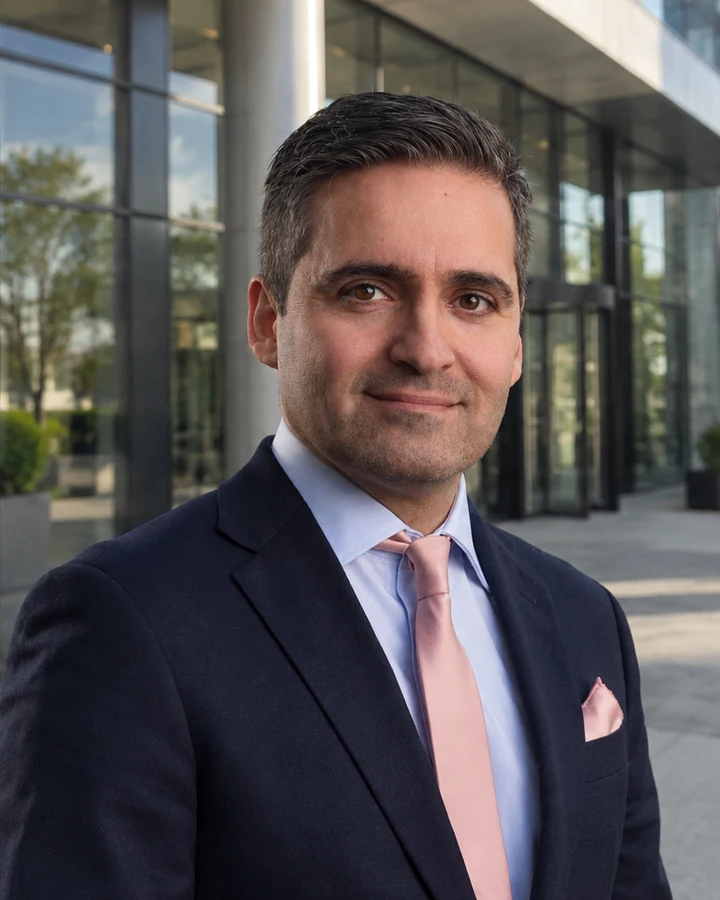
Managing Partner · Lead Auditor
5 years of executive experience in cybersecurity, 8 years of ISMS responsibility and experience with certification projects. Certified ISO 27001 Lead Auditor.
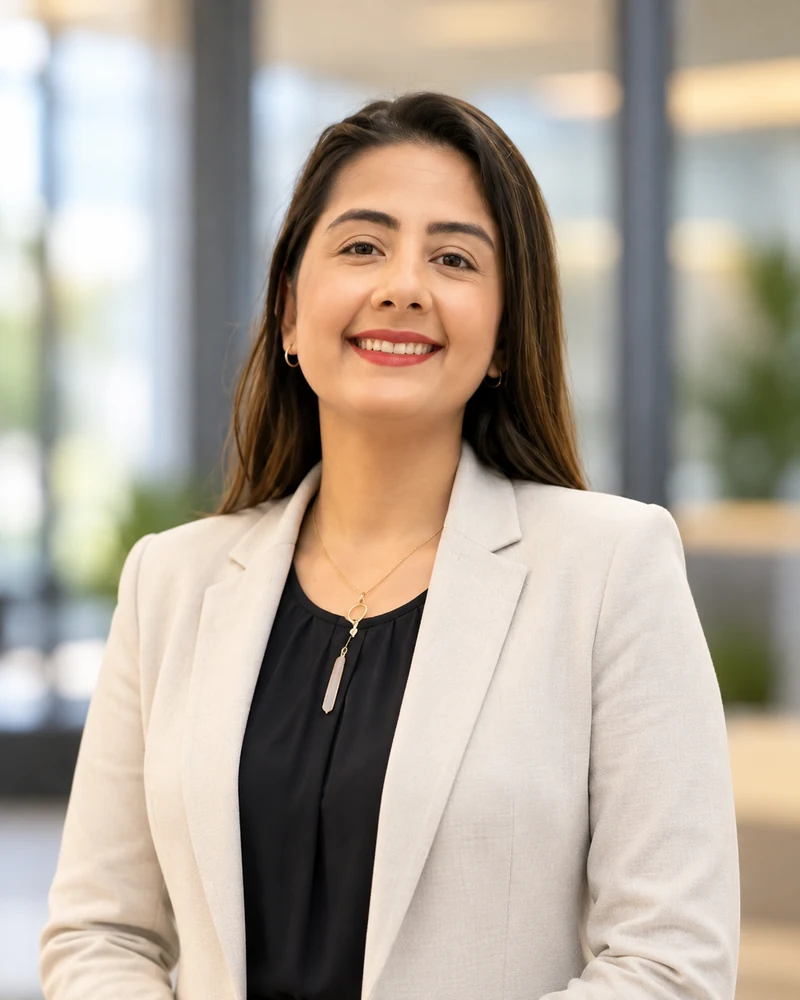
Legal & Compliance
Experience running an independent legal practice, with expertise in legal matters and compliance.
The same management logic across information security, cybersecurity regulation and AI governance.
Understand scope, current control and evidence.
Focus on material gaps, risk and external pressure.
Assign owners and build controls into normal operations.
Test effectiveness and keep the system improving.
Governancy is a good fit for organisations that need senior expertise, practical decisions and demonstrable control without creating unnecessary dependencies.
If the problem needs a programme, we will say so. If it needs a focused intervention, we will keep it focused.
Request a free scope check